Mobile Robot Cybersecurity: What to check before buying
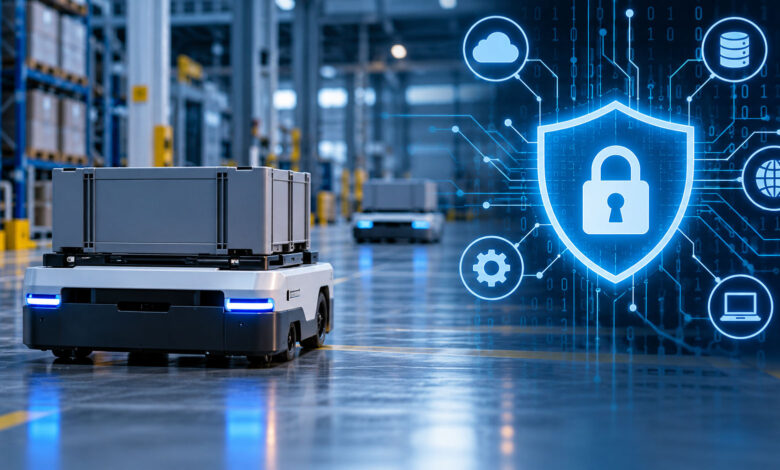
Buying a mobile robot directly from a Chinese manufacturer, without going through a European integrator, requires the industrial company to take responsibility for a greater number of checks.
Beyond performance and price, it must examine data flows, remote access, software updates and maintenance conditions. A connected robot also becomes part of the industrial IT system.
Consider the case of a French company purchasing mobile robots directly from a Chinese manufacturer to equip its factory or warehouse. It compares payload capacity, battery life, navigation accuracy and price. But before connecting these machines to the site network, it must also understand their digital architecture.
Can the robots operate without a connection to the manufacturer’s cloud? Do site maps, images and diagnostic data remain within the company? Who can access the machines remotely, from which countries and with what permissions? How are updates validated?
Without a European integrator, the company must organize these checks itself or entrust them to a specialist. However, the presence of an integrator does not, by itself, guarantee cybersecurity: the scope of its intervention, its expertise and its responsibilities must be clearly defined.
To identify manufacturers, integrators and industry specialists, companies can consult the robotics professional directory. However, the provider’s specific expertise in industrial cybersecurity should still be verified before any intervention.
The Chinese nationality of the manufacturer is not, in itself, a vulnerability. However, a lack of documentation, opaque communications or the inability to revoke remote access are concrete criteria that should be examined before purchase.
For the industrial company, the question is simple: after installation, who controls the robots, their data and their connections?
An Attack Surface That Extends Beyond the Robot
An AMR, or autonomous mobile robot, rarely operates on its own. Depending on its architecture, it communicates with a fleet management server, a supervision interface, a warehouse management system and maintenance services. The perimeter to be assessed therefore also includes administration workstations, network equipment and software interfaces.
NIST points out that OT systems technologies that monitor or control physical processes have specific availability, reliability and safety constraints. A cyber compromise must therefore be assessed in terms of its potential operational consequences.
Consider a hypothetical scenario: a compromised maintenance account provides access to the fleet manager. Depending on the permissions granted, an attacker could view information, modify missions or interrupt operations.
This does not mean that the attacker could automatically disable the robots’ physical safety protections. However, immobilizing a fleet may already be enough to disrupt the supply of a production line.
The assessment should therefore cover data confidentiality, configuration integrity, service availability and the possibility of propagation to other systems.
Understand Which Data Leaves the Site
Depending on the sensors and functions enabled, a robot may generate factory maps, images, mission logs and diagnostic information. Not all of this data necessarily leaves the site. The supplier should specify which information is processed locally and which is transmitted externally.
For each external communication flow, the buyer should know the destination, purpose, transmitted content and activation conditions. The company should also identify the service providers involved, retention periods and the consequences of disabling the service.
Encryption protects data while it is being transmitted. However, it does not, by itself, answer questions about how the data will be used or who may access it once it reaches its destination.
One key document to request is a data-flow matrix showing sources, destinations, ports, protocols and purposes. This documentation should be compared with the communications actually observed during a pilot project, particularly during a software update or a support intervention.
A connection to an external server is not automatically suspicious. However, an unexplained or uncontrollable connection requires further investigation.
Control Remote Maintenance Access
Remote maintenance can reduce diagnostic time. However, it becomes a sensitive issue when access remains permanently open, relies on a shared account or is not visible to the operator.
For a robotics project, Robot Magazine recommends named user accounts, multifactor authentication at the remote maintenance access point and permissions limited to the operations that are actually required.
Sessions should be authorized for a defined period and generate usable logs. The company must be able to identify the person carrying out the intervention, determine which systems are accessible and revoke access when necessary.
A VPN secures a communication channel. It does not guarantee that the user’s permissions are appropriate or that access is sufficiently restricted.
When robots are purchased directly, these arrangements must be negotiated with the manufacturer before deployment. In particular, the agreement should specify who authorizes interventions and who retains the access logs.
Isolate Robots Without Disrupting Their Operation
Placing robots on a dedicated VLAN provides an initial level of network separation. However, communications between this network, the fleet server and the company’s other applications must also be filtered.
The recommended approach is to identify the communications required for normal operation and authorize only those flows. Administration interfaces should be accessible only from controlled workstations or controlled access points.
Network segmentation must be verified in practice: an overly permissive rule between networks can eliminate the apparent benefit of separation.
The pilot project should also test system dependencies. What happens when the cloud becomes unavailable, when the Wi-Fi connection is lost or when the fleet server restarts?
The answers should specify which functions remain available, the state adopted by the robots and the conditions required to resume operations. These behaviors must be compatible with the site’s safety and business continuity requirements.
ROS 2 Does Not Eliminate the Need to Check Configuration
For equipment using ROS 2, the name of the middleware itself is not a guarantee of cybersecurity. Research into SROS2 presents tools and methods for securing ROS 2 communications and graphs while also highlighting the challenges involved in implementation.
The buyer should ask which protections are actually deployed: participant authentication, communication permissions, encryption and certificate management.
The system’s behavior should also be examined when a certificate expires or when a security configuration becomes invalid.
This analysis does not replace the examination of the operating system, web interfaces, APIs and third-party components. Security must be assessed on the configuration that is actually delivered.
Plan for Updates Throughout the Entire Operating Life
The company must understand how the robot verifies the origin and integrity of an update, who is authorized to initiate it and how the installation is logged.
Signing an update package helps protect against unauthorized modification. However, it does not guarantee that the new version is free from vulnerabilities or compatible with every configuration used on the site.
The process should include prior validation, a defined maintenance window and a recovery procedure. Any rollback mechanism must remain controlled to avoid reinstalling a vulnerable version.
The duration of software support deserves particular attention. For a machine expected to operate for ten years, the contract should specify the end date of maintenance, the conditions for correcting vulnerabilities and the solutions offered when support ends.
Vendor dependency should also be anticipated: can the company back up its configurations, retrieve its data and continue certain operations if a remote service disappears?
Distinguish Cybersecurity From Physical Safety
The cybersecurity analysis must examine the interfaces between control, supervision and safety functions. Which configurations can be modified remotely?
Which protections remain in place if communications are lost or compromised?
A penetration test does not replace the validation of robotic safety functions. Conversely, the presence of physical safety devices does not demonstrate that IT access and data are properly controlled.
Tests that may cause movement, shutdown or degradation should be prepared with the manufacturer and carried out in a controlled environment.
The objective is to verify the possible consequences of an incident without putting people or the installation at risk.
The European Regulatory Timeline Must Be Anticipated
The Cyber Resilience Act introduces cybersecurity requirements for products with digital elements that fall within its scope.
Its main obligations will apply from 11 December 2027. The reporting obligations for actively exploited vulnerabilities and serious incidents have applied since 11 September 2026.
For a robotics purchase intended for a French site, the supplier should be asked how it is preparing the product concerned for compliance. A general statement about CRA readiness does not replace technical documentation or an assessment of the actual installation.
Evidence to Request Before Signing
For a direct purchase without a European integrator, the industrial company should obtain at least:
- An architecture diagram and a communication-flow matrix.
- A description of the data collected, its destination and retention period.
- Documented rules for authorizing and revoking remote access.
- Procedures for updates, backups and restoration.
- Precise commitments regarding the duration and conditions of software support.
- A vulnerability-reporting contact and a remediation process.
- Documented tests covering connection loss and service recovery.
- When an audit is provided, a report specifying the versions tested, scope, limitations and verification of corrective actions.
The purchasing decision should be based on these verifiable elements. An attractive price is not enough: the total cost of a robotics project must also include network connectivity, cybersecurity controls, technical support, software updates and maintenance. These costs can significantly reduce the initial financial advantage of a direct purchase.
FAQ – Cybersecurity for Mobile Robots Purchased Directly from a Chinese Manufacturer
2. What data can an AMR transmit outside the company?
An autonomous mobile robot can generate factory maps, images, mission logs and diagnostic information. Buyers should determine exactly which data remains on site, which data is transmitted externally, where it goes and why. A communication flow matrix can help document and verify these exchanges.
3. How can remote maintenance of an industrial robot be secured?
Remote access should use individual accounts, multi-factor authentication and permissions limited to necessary operations. Sessions should also be time-limited, logged and revocable by the operator. A VPN can secure the communication channel, but it does not guarantee that user permissions are appropriately restricted.
4. Should mobile robots be isolated from the rest of the industrial network?
Placing robots on a dedicated VLAN provides an initial level of separation, but this alone is not sufficient. Communications between the robots, fleet management server and other company applications should be filtered so that only the connections required for operation are authorized.
5. Does ROS 2 guarantee the cybersecurity of a robot?
No. Using ROS 2 does not automatically make a robotic system secure. Companies should verify the protections actually deployed, including authentication, communication permissions, encryption and certificate management, as well as the security of the operating system, APIs and third-party components.
6. Why should a robot’s software update policy be reviewed before purchase?
Industrial robots may remain in operation for many years. Buyers should therefore understand the duration of software support, vulnerability remediation procedures, backup and recovery mechanisms, and what happens if a remote service becomes unavailable.
7. What cybersecurity documentation should be requested from the manufacturer before purchase?
For a direct purchase without a European integrator, companies should request an architecture diagram, communication flow matrix, description of collected data, remote-access rules, update and recovery procedures, software support commitments and a vulnerability management process. Documented tests covering connectivity loss and service recovery should also be requested.